Architecture
The diagram summarizes the primary traffic flow, application components, security controls, automation, and data services used by the project.
Infrastructure · Cloud Architecture · Zero-Trust Security
Strong foundation in server administration, systems engineering, and networking, with hands-on experience supporting reliable business infrastructure. Experienced in maintaining system stability, critical services, secure connectivity, and operational continuity.
Designing scalable, automated environments across AWS & Azure. Bridging legacy on-prem systems with high-availability cloud infrastructure through IaC, CI/CD automation, and resilient multi-region deployments prioritizing performance, scalability, and operational continuity.
Architecting Zero-Trust security frameworks and automating IAM at scale across hybrid and cloud-native environments. Focused on building resilient, adaptive security models that proactively protect systems, identities, and access layers through automation, policy enforcement, and continuous validation.
An sporting goods e-commerce platform showcasing an enterprise-grade infrastructure and modern cloud architecture. Focuses on scalability, observability, containerized deployments, disaster recovery, cloud design. It includes a Next.js storefront and admin applications backed by PostgreSQL database and Prisma ORM.
A hybrid-architecture web application, using a static S3-hosted frontend and a scalable serverless backend. Used AWS Lambda and API Gateway to execute dynamic processing, optimizing infrastructure costs. Strengthened security by migrating sensitive API credentials to protected Lambda Environment Variables.
Migration of a Sporting E-commerce Platform to AWS, mapping workloads to cloud-native services for performance, scalability, and reliability. Backed by Amazon EC2, Auto-scaling, Neon PostgreSQL DB. CI/CD pipeline is configred with Github Actions, new deployments build isoloted AMI artifacts. Infrastructure is deployed and mangaged by Terraform IaC.
Sporting E-commerce Platform migration to Azure using a containerized architecture. Terraform provisions the infrastructure, while Azure DevOps CI/CD builds, pushes, and deploys container images through Azure Container Registry to Azure Container Apps. Scalability, security, monitoring, and high availability built into the design.
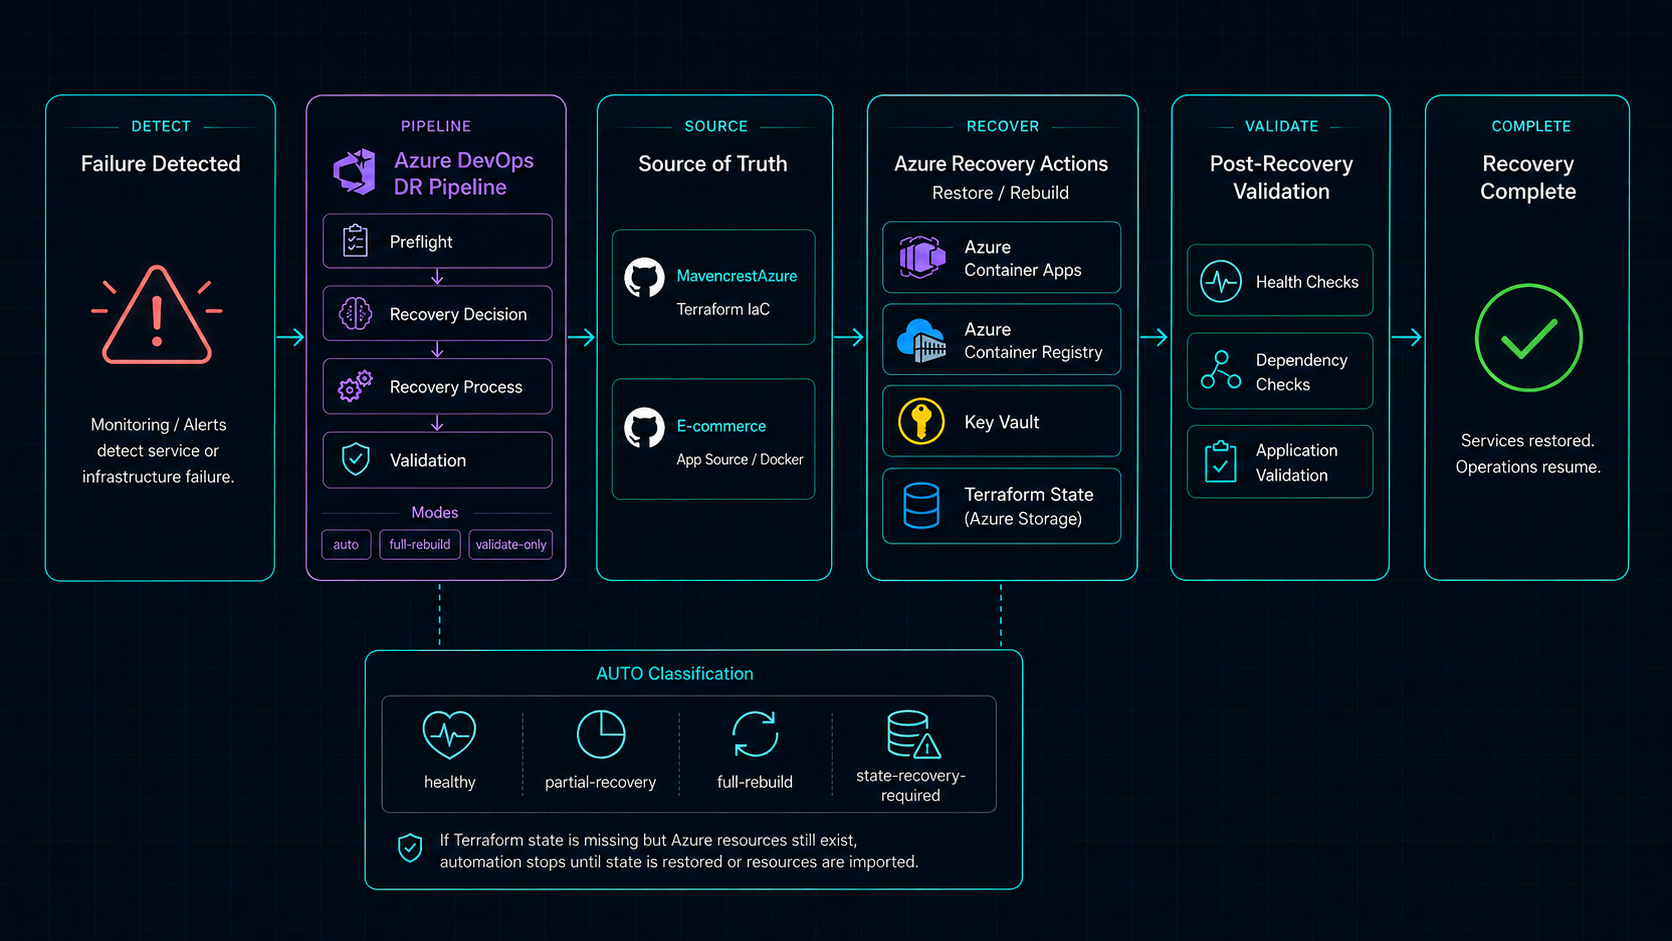
Disaster recovery orchestration for the Mavencrest Azure container platform. This repository handles a full recovery using two repositories as its source of truth: MavencrestAzure — Terraform IaC E-commerce - Application source and Docker images. DR orchestration pipeline runs depending on level of failure detected.
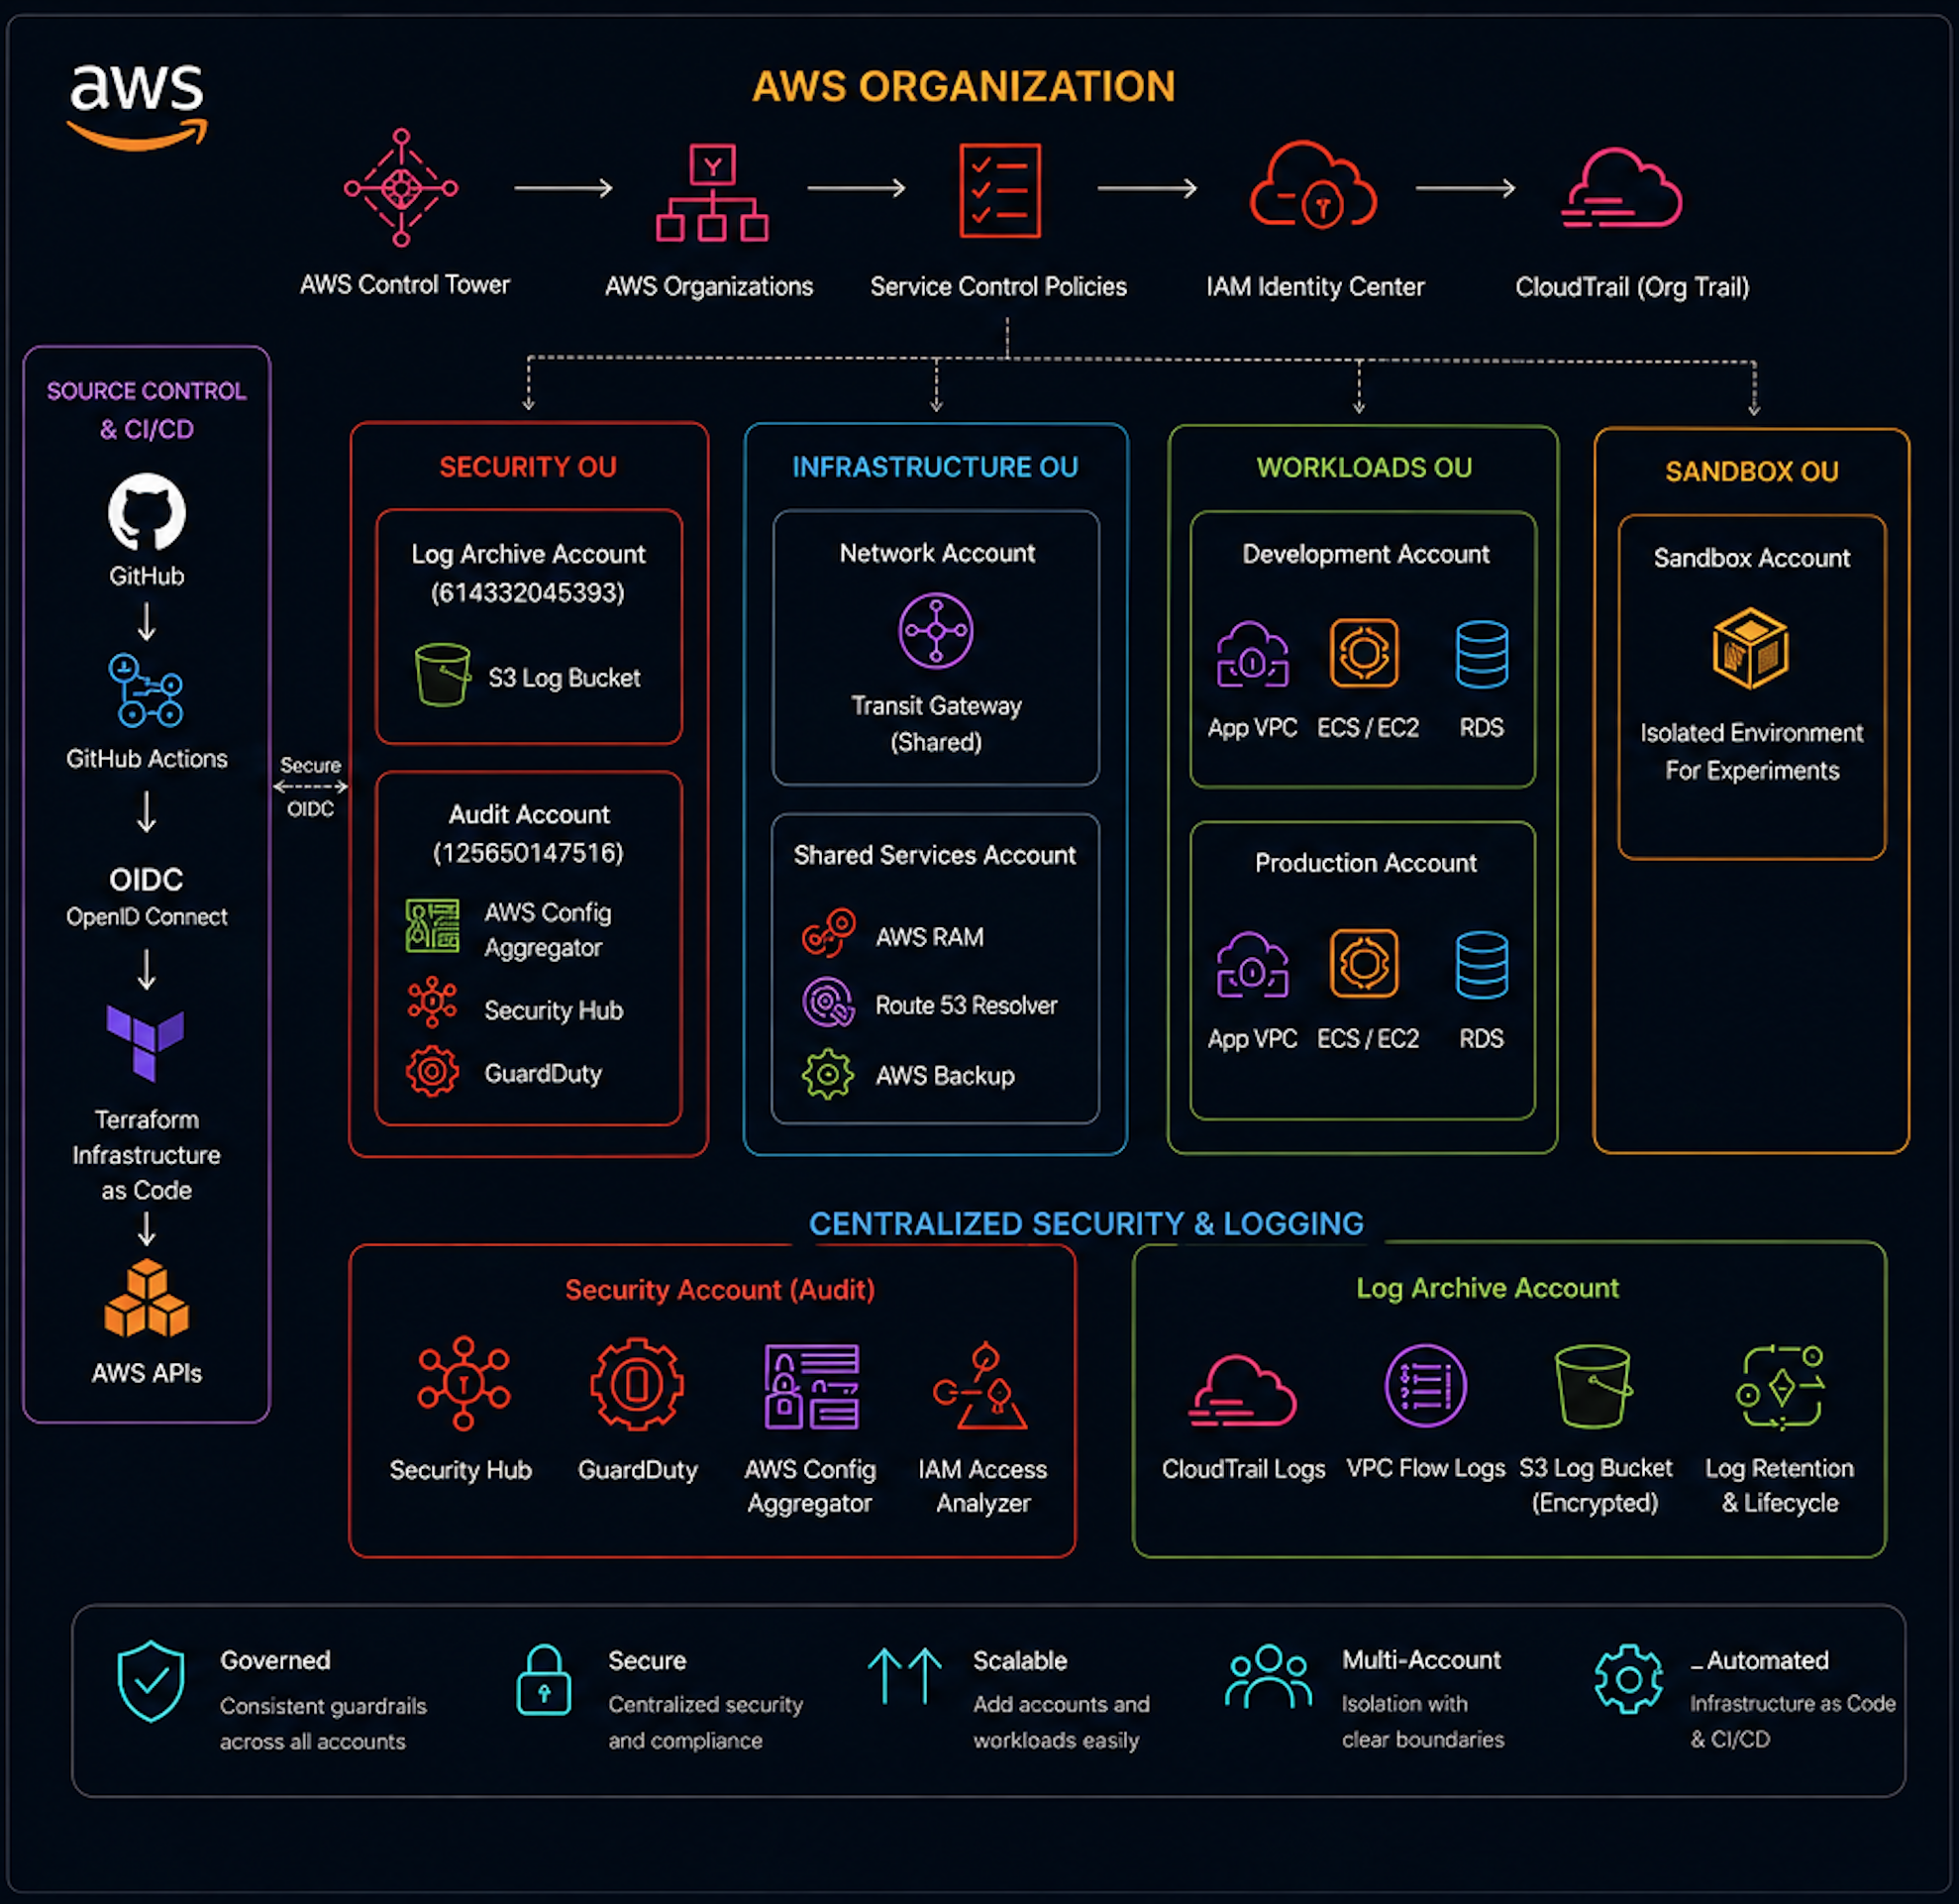
Automated provisioning of a secure, multi-account AWS environment using Terraform and AWS Control Tower to enforce governance and scalable cloud architecture. This includes Service Control Policies, security guard rails, IAM permission boundaries, and centralized identity management.
A secure, scalable Azure cloud foundation using Terraform, incorporating Azure Policy, management groups, RBAC, identity governance, security guardrails, and centralized resource management to enforce governance across environments.
A Kubernetes deployment of a containerized e-commerce application featuring horizontal pod autoscaling, rolling updates, service discovery.
Cloud based CI/CD pipeline that automatically builds, tests, scans, and verifies Docker images for vulnerabilities before they can ever be deployed.
Monitor, aggregate data, and observe an entire Mavencrest ecosystem. ex: container health—into. Visualization Layer with Grafana
Cloud cost governance platform providing real-time spend visibility, budget management, reporting, resource optimization, and savings recommendations across multi-cloud environment.
Secure infrastructure across cloud and hybrid environments, focusing on identity-first security, network hardening, and least-privilege access controls. Focuses on security best practices including IAM governance and continuous monitoring.
A production-ready sporting goods e-commerce platform built with separate Next.js storefront and administration applications, Google OAuth and email/password authentication, Docker support, nginx, PostgreSQL, and Prisma 7 ORM.
Production-ready
The diagram summarizes the primary traffic flow, application components, security controls, automation, and data services used by the project.
This project is presented as an engineering case study focused on reliability, scalability, security, repeatability, and operational clarity.
Add implementation screenshots, Terraform plans, deployment output, monitoring views, design trade-offs, and lessons learned as the project progresses.
A hybrid web application that separates a static frontend from an AWS serverless backend. API Gateway invokes Lambda for dynamic processing while credentials remain protected in Lambda.
Production-ready
The diagram summarizes the primary traffic flow, application components, security controls, automation, and data services used by the project.
This project is presented as an engineering case study focused on reliability, scalability, security, repeatability, and operational clarity.
Add implementation screenshots, Terraform plans, deployment output, monitoring views, design trade-offs, and lessons learned as the project progresses.
A Kubernetes deployment of a containerized e-commerce workload demonstrating ingress routing, service discovery, rolling updates, horizontal pod autoscaling, and high availability.
In progressThe diagram summarizes the primary traffic flow, application components, security controls, automation, and data services used by the project.
This project is presented as an engineering case study focused on reliability, scalability, security, repeatability, and operational clarity.
Add implementation screenshots, Terraform plans, deployment output, monitoring views, design trade-offs, and lessons learned as the project progresses.
A governed multi-account AWS foundation using Terraform and AWS Control Tower with centralized identity, Service Control Policies, permission boundaries, logging, and regional guardrails.
In progressThe diagram summarizes the primary traffic flow, application components, security controls, automation, and data services used by the project.
This project is presented as an engineering case study focused on reliability, scalability, security, repeatability, and operational clarity.
Add implementation screenshots, Terraform plans, deployment output, monitoring views, design trade-offs, and lessons learned as the project progresses.
A secure cloud and hybrid infrastructure design centered on identity-first controls, network segmentation, least privilege, centralized monitoring, and policy enforcement.
In progressThe diagram summarizes the primary traffic flow, application components, security controls, automation, and data services used by the project.
This project is presented as an engineering case study focused on reliability, scalability, security, repeatability, and operational clarity.
Add implementation screenshots, Terraform plans, deployment output, monitoring views, design trade-offs, and lessons learned as the project progresses.
A secure container delivery pipeline that builds, tests, scans, verifies, and publishes Docker images to Azure Container Registry before deployment.
In progressThe diagram summarizes the primary traffic flow, application components, security controls, automation, and data services used by the project.
This project is presented as an engineering case study focused on reliability, scalability, security, repeatability, and operational clarity.
Add implementation screenshots, Terraform plans, deployment output, monitoring views, design trade-offs, and lessons learned as the project progresses.
A production-style migration of the e-commerce platform to AWS using Terraform, EC2 Auto Scaling, an Application Load Balancer, VPC networking, object storage, and PostgreSQL.
Production-ready
The diagram summarizes the primary traffic flow, application components, security controls, automation, and data services used by the project.
This project is presented as an engineering case study focused on reliability, scalability, security, repeatability, and operational clarity.
Add implementation screenshots, Terraform plans, deployment output, monitoring views, design trade-offs, and lessons learned as the project progresses.
An Azure migration solution using Azure Functions and API Management to provide a scalable, decoupled backend with managed security and minimal server administration.
Production-ready
The diagram summarizes the primary traffic flow, application components, security controls, automation, and data services used by the project.
This project is presented as an engineering case study focused on reliability, scalability, security, repeatability, and operational clarity.
Add implementation screenshots, Terraform plans, deployment output, monitoring views, design trade-offs, and lessons learned as the project progresses.
A centralized telemetry platform designed to ingest infrastructure and application data, process it through a shared pipeline, and visualize health, usage, errors, and operational trends.
In progressThe diagram summarizes the primary traffic flow, application components, security controls, automation, and data services used by the project.
This project is presented as an engineering case study focused on reliability, scalability, security, repeatability, and operational clarity.
Add implementation screenshots, Terraform plans, deployment output, monitoring views, design trade-offs, and lessons learned as the project progresses.
A multi-cloud cost governance platform providing spend visibility, budgets, chargeback and showback, optimization findings, and actionable savings recommendations.
In progressThe diagram summarizes the primary traffic flow, application components, security controls, automation, and data services used by the project.
This project is presented as an engineering case study focused on reliability, scalability, security, repeatability, and operational clarity.
Add implementation screenshots, Terraform plans, deployment output, monitoring views, design trade-offs, and lessons learned as the project progresses.
A cloud-based backup and disaster recovery design with policy-driven backups, cross-region replication, recovery orchestration, testing, and failover.
In progressThe diagram summarizes the primary traffic flow, application components, security controls, automation, and data services used by the project.
This project is presented as an engineering case study focused on reliability, scalability, security, repeatability, and operational clarity.
Add implementation screenshots, Terraform plans, deployment output, monitoring views, design trade-offs, and lessons learned as the project progresses.
An enterprise-ready Azure Landing Zone built with Terraform, management groups, Azure Policy, RBAC, central logging, networking, governance controls, and GitHub OIDC.
In progressThe diagram summarizes the primary traffic flow, application components, security controls, automation, and data services used by the project.
This project is presented as an engineering case study focused on reliability, scalability, security, repeatability, and operational clarity.
Add implementation screenshots, Terraform plans, deployment output, monitoring views, design trade-offs, and lessons learned as the project progresses.
Validates advanced technical skills and experience in designing distributed applications and systems on the AWS platform. Focuses on complex multi-tier architecture strategy, cost optimization, scaling, and enterprise migration frameworks.
Validates technical expertise in deployment, management, security, and operations on the AWS platform. Confirms a strong understanding of system health monitoring, infrastructure automation, and resource provisioning.
Demonstrates comprehensive knowledge of designing high-availability, cost-effective, and fault-tolerant distributed systems across AWS core services, focusing on compute, storage, networking, and security layers.
Demonstrates technical proficiency in developing, deploying, and debugging cloud-native applications using AWS development tools, SDKs, serverless resources, and CI/CD pipelines.
Validates foundational knowledge of network infrastructure, covering IP connectivity, IP services, security fundamentals, automation, programmability, and routing/switching protocols.
Validates enterprise-level skills required to implement, manage, and monitor identity, governance, storage, compute, and virtual networks in a cloud environment.
Demonstrates baseline foundational understanding of cloud concepts, core Azure architecture models, management tools, compliance frameworks, and network security infrastructure options.
Proves proficiency in managing files, controlling the command-line shell, configuring local storage, managing user accounts, and validates essential skills in system security.
Validates the ability to automate Linux environment tasks using Ansible Automation Platform. It proves the ability to manage, configure, and provision multiple systems at scale through infrastructure-as-code
Establish a secure communication line or explore professional links.